Chris Sanders Applied Network Security Monitoring Review: Builds Core Skills for SOC Analysts
Applied Network Security Monitoring by Chris Sanders is a comprehensive, practical guide that systematically teaches the collection, detection, and analysis stages of NSM, making it a foundational resource for new and working analysts.
 By Elvis Dicki
Updated October 21, 2026
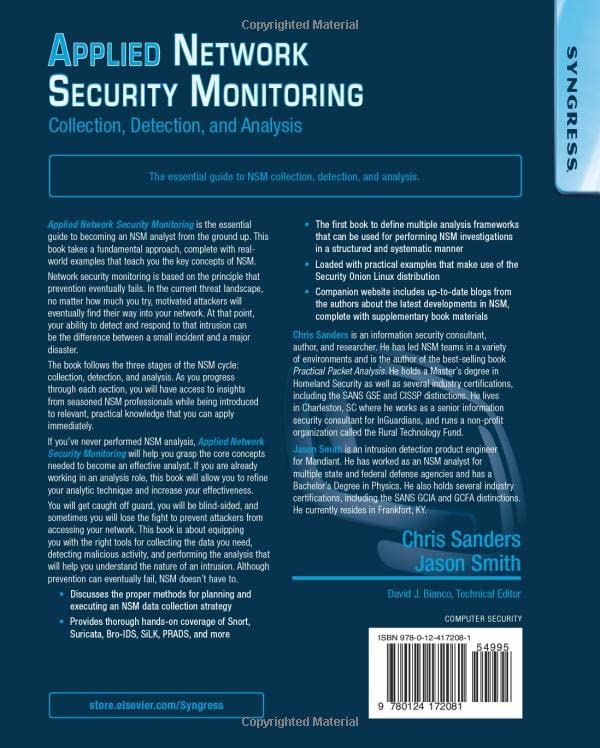
In the cybersecurity landscape, where prevention inevitably fails, the ability to detect and respond to intrusions becomes the critical line of defense. Chris Sanders Applied Network Security Monitoring is the essential guidebook for building that capability from the ground up. This book is specifically designed for individuals aiming to become effective Network Security Monitoring (NSM) analysts, whether they are just starting their journey or are seasoned professionals looking to refine their techniques. Its bottom line is clear: it provides a structured, practical framework for mastering the core skills of collection, detection, and analysis using real-world tools and examples.

The book’s approach is fundamentally hands-on, guiding readers through the entire NSM cycle with insights from experienced professionals. It demystifies the process of security investigations, moving beyond theoretical concepts to actionable knowledge. By focusing on the Security Onion Linux distribution and tools like Snort and Suricata, it equips readers with the methodologies needed to understand and respond to threats effectively, making it a cornerstone resource for anyone involved in defensive security operations or studying for certifications like the GIAC Certified Intrusion Analyst (GCIA).
Prime Applied Network Security Monitoring
As an Amazon Associate we earn from qualifying purchases. Product prices and availability are accurate as of the date/time indicated.
Chris Sanders Applied Network Security Monitoring at a Glance
| Specification | Detail |
|---|---|
| Publisher | Syngress |
| Publication Date | December 19, 2013 |
| Edition | 1st |
| Print Length | 496 pages |
| ISBN-10 | 0124172083 |
| Item Weight | 2.31 pounds |
| Dimensions | 7.5 x 1.12 x 9.25 inches |
| Best Sellers Rank | #111 in Computer Networks, #504 in Computer Network Security |
| Customer Rating | 4.8 out of 5 stars |
Design and Build
As a technical textbook, the design of Chris Sanders Applied Network Security Monitoring prioritizes clarity and thoroughness over flashy presentation. The 496-page volume is substantial, with dimensions typical of a comprehensive reference guide. The physical build is robust, with a weight that signifies its dense, information-packed content. The structure of the book itself mirrors its pedagogical approach: it is systematically organized to guide the reader from foundational concepts through to advanced analysis techniques. The layout facilitates learning, with clear chapter divisions that correspond to the three core stages of the NSM cycle. This logical progression makes it easy to follow and use as both a sequential learning tool and a reference for specific topics.
Performance and Features
Comprehensive Coverage of the NSM Cycle
The book’s primary performance metric is its educational value, and it excels by covering the full spectrum of Network Security Monitoring. It is meticulously divided into the three critical stages: collection, detection, and analysis. This tripartite structure ensures readers build a complete understanding, starting with how to plan and execute a data collection strategy, moving through the hands-on use of detection tools, and culminating in systematic analysis frameworks for investigations. This end-to-end coverage is its standout feature, providing a holistic view of the NSM analyst’s role.
Practical, Hands-On Techniques
Unlike purely theoretical texts, this book is loaded with practical examples that utilize the Security Onion Linux distribution. It provides thorough hands-on coverage of essential NSM tools including Snort, Suricata, Bro-IDS, SiLK, and PRADS. This practical focus allows readers to apply the techniques immediately, bridging the gap between knowledge and real-world application. The examples are designed to be relevant and actionable, teaching key concepts through direct engagement with the tools analysts use daily.
Structured Analysis Frameworks
A key innovation of the book is its definition of multiple analysis frameworks. It provides readers with structured, systematic methodologies for performing NSM investigations. This moves analysis from an ad-hoc art to a more repeatable science, helping analysts ensure thoroughness and consistency in their work. These frameworks are a significant value-add for both new analysts seeking guidance and experienced professionals looking to standardize and improve their processes.
Setup, Support and Ownership
To get the full benefit from the exercises in Applied Network Security Monitoring, readers need access to a Linux environment, specifically the Security Onion distribution mentioned throughout the text. This requirement means the book is best paired with a lab setup where tools can be installed and configurations tested. The publisher provides a companion website with supplementary materials and blogs from the authors about the latest developments in NSM, which is crucial for ongoing learning as the field evolves. It is important to note that for complete updates and the most current tool information, these companion resources are necessary, as the print edition was published in 2013. The book assumes a base level of networking knowledge, so it is most suitable for those with some prior experience or who are willing to supplement with foundational networking resources. For more foundational learning, explore our guide to the best cybersecurity books for beginners.
What Owners Say
Owner feedback for Applied Network Security Monitoring is overwhelmingly positive, reflected in its high rating where the vast majority of reviews are five-star. Readers consistently praise it as an “amazingly easy read” that maintains a conversational and entertaining tone despite its technical depth, setting it apart from drier textbooks. It is frequently described as “thorough” and “immediately applicable,” with many highlighting its value as a perfect study companion for the GCIA certification, noting its superior organization and breakdown of packet analysis. Owners in Security Operations Center (SOC) roles call it a “must-read,” appreciating how it walks through establishing an NSM capability and staffing a SOC. The common thread is that the book is written by analysts for analysts, providing practical, real-world knowledge that is both comprehensive and accessible. However, some advanced readers caution that a solid understanding of basic networking dynamics is a prerequisite to get the most from the content.
Pros and Cons
Pros
- Comprehensive coverage of the full NSM cycle: collection, detection, and analysis.
- Practical examples tied to the Security Onion distribution for immediate application.
- Suitable for both beginners and working analysts looking to refine their skills.
- Defines structured analysis frameworks for systematic investigations.
- Clear, conversational writing style that is easy to read and understand.
- Excellent resource for those studying for certifications like the GCIA.
Cons
- Requires access to a Linux environment for full hands-on exercises.
- Companion website materials are needed for the most current updates and information.
- Assumes a basic level of networking knowledge as a starting point.
- Print edition is from 2013, so some tool specifics may require supplemental research.
- Not a book for absolute beginners with zero IT or networking background.
- Focused heavily on NSM; other security domains are not covered.
Who Should Buy It (and Who Should Skip It)
This book is an ideal purchase for aspiring Network Security Monitoring analysts, cybersecurity students, and professionals working in or transitioning to SOC roles. It is perfectly suited for individuals preparing for the GIAC Certified Intrusion Analyst (GCIA) certification, as owners confirm it aligns closely with that curriculum. IT professionals with basic networking knowledge who want to deepen their understanding of defensive security and intrusion detection will find immense value. It also serves as a great reference for security managers seeking to understand the analyst’s process or establish NSM practices.
Those who should consider skipping it or starting with more foundational material include complete beginners with no prior networking or IT experience, as the book assumes this base knowledge. Individuals looking for a broad, general cybersecurity overview or information on other security domains like endpoint protection or governance will not find it here, as its focus is specifically and deeply on NSM. If you cannot or will not set up a Linux lab environment to follow the practical exercises, a significant portion of the book’s value will be lost. For those seeking a wider perspective on tech tools, our Tech Gear section covers a broader range of products.
Final Verdict
Chris Sanders Applied Network Security Monitoring stands as a foundational and highly effective guide to the critical discipline of detecting and responding to network intrusions. Its greatest strength is its practical, systematic approach to the entire NSM cycle, empowering readers with not just knowledge, but applicable skills using tools like Snort and Suricata within the Security Onion environment. The book successfully bridges the gap between theory and practice, providing structured analysis frameworks that elevate the work of an analyst from reactive to methodical.
While its publication date means some tool specifics may need to be supplemented via the companion website, the core principles, methodologies, and analytical frameworks it teaches remain timeless and essential. The overwhelmingly positive owner feedback, highlighting its clarity and immediate applicability, is a strong testament to its quality. For anyone serious about building or refining their network security monitoring capabilities, whether for career advancement, certification study, or improving their organization’s defensive posture, this book is an indispensable resource. It delivers precisely on its promise: equipping you with the right tools and techniques for when prevention fails.
FAQs
Is this book suitable for complete beginners in cybersecurity?
While the book takes a fundamental approach to NSM, it assumes the reader has basic networking knowledge. It is excellent for beginners to the specific field of network security monitoring, but not for absolute beginners to IT or networking concepts. Those without this foundation should first build their networking skills before tackling this material.
How relevant is the content since the book was published in 2013?
The core principles, analysis frameworks, and cycle of collection, detection, and analysis taught in the book remain highly relevant and foundational. However, specific details about tool versions and some configurations may be dated. The authors maintain a companion website with blogs and supplementary materials to help address updates in the NSM field, which readers should utilize.
Do I need special equipment or software to use this book?
To complete the hands-on exercises and get the full practical value, you will need access to a computer where you can run a Linux environment, specifically the Security Onion distribution that the book’s examples are based on. Setting up a lab, either virtually or on dedicated hardware, is recommended.
Is this book helpful for professional certification exams?
Yes, numerous owner reviews specifically highlight this book as a perfect study companion for the SANS SEC503 course and the GIAC Certified Intrusion Analyst (GCIA) certification. Readers praise its organization and breakdown of packet analysis as being immediately applicable to that certification path. For more expert picks on specialized tools and resources, check out our Blog.
About the author

Elvis Dicki writes reviews and buying guides for CyberSecLabs.