Bragley Johnvigs Advanced Windows DFIR Techniques Review: A 208-Page Guide to Memory Forensics
This comprehensive guide dives deep into memory forensics, registry analysis, and threat containment for Windows security professionals, offering practical skills through hands-on tutorials and real-world case studies.
 By Elvis Dicki
Updated October 21, 2026
In the complex and ever-evolving world of cybersecurity, the ability to dissect a digital crime scene on Windows platforms is a critical skill. The Bragley Johnvigs Advanced Windows DFIR Techniques book positions itself as a dedicated resource for IT professionals and cybersecurity analysts seeking to master these investigative methods. This guide aims to transform readers from novices into capable investigators by providing cutting-edge skills in memory forensics, registry analysis, event log scrutiny, and rapid threat containment. It is a focused manual for those who need to outmaneuver attackers and safeguard Windows systems with precision.

This book covers a wide spectrum of Digital Forensics and Incident Response (DFIR) topics, from foundational concepts to advanced techniques for handling sophisticated breaches like ransomware and Advanced Persistent Threats (APTs). The bottom line is that this resource offers a consolidated, practical approach to Windows DFIR, emphasizing the correlation between different data artifacts to build a complete investigative picture, though it does assume some prior technical knowledge of Windows systems.
Prime Advanced Windows DFIR Techniques
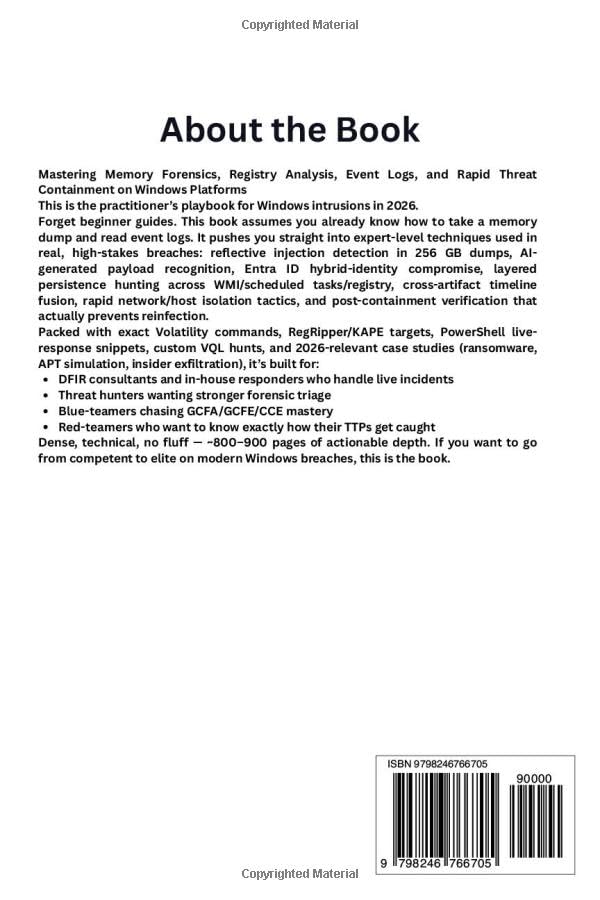
As an Amazon Associate we earn from qualifying purchases. Product prices and availability are accurate as of the date/time indicated.
Bragley Johnvigs Advanced Windows DFIR Techniques at a Glance
| Specification | Detail |
|---|---|
| Publisher | Independently published |
| Publication Date | February 3, 2026 |
| Language | English |
| Print Length | 208 pages |
| ISBN-13 | 979-8246766705 |
| Item Weight | 13.3 ounces |
| Dimensions | 6 x 0.47 x 9 inches |
| Best Sellers Rank | #4,183,084 in Books; #4 in Windows Registry; #192 in Windows Server Guides; #360 in Microsoft OS Guides |
Design and Build
As a published book, its design is centered on content organization and readability rather than physical hardware components. The product specifications indicate a standard paperback format with a print length of 208 pages, suggesting a substantial but not overwhelming volume of content. The dimensions of 6 by 9 inches are typical for technical manuals, offering a comfortable reading experience. Weighing 13.3 ounces, it is lightweight enough for portability. The build quality of independently published books can vary, but the focus here is squarely on the internal structure of the knowledge presented—organizing complex DFIR concepts into a logical, progressive learning path from fundamentals to advanced case studies.
Performance and Features
Core DFIR Coverage
The book’s performance is measured by the depth and utility of its instructional content. It promises comprehensive coverage of key Windows DFIR domains. A primary feature is its deep dive into memory forensics, teaching readers to acquire volatile data using tools like FTK Imager and DumpIt, and then analyze memory dumps with frameworks like Volatility to uncover hidden processes, injected code, and network artifacts that disk forensics might miss. This is paired with extensive registry forensics, explaining the binary structure of hive files and how to track user activities and persistence mechanisms through critical keys.
Integrated Analysis and Automation
Another significant performance aspect is the emphasis on correlation. The book instructs on integrating findings from memory, the registry, and Windows event logs to build accurate, irrefutable timelines of attacker activity. It covers parsing event logs for specific security indicators and event IDs that signal malicious behavior. To enhance response speed, a featured capability is the development of automated workflows using PowerShell scripting, aimed at streamlining repetitive DFIR tasks for faster incident response. This practical approach is designed to translate reading into actionable skill.
Real-World Application and Future-Proofing
The feature set is rounded out with applied learning. The book includes real-world case studies on incidents like ransomware and APT infiltrations, allowing readers to apply techniques in a contextual, step-by-step manner. It also addresses the critical soft skills of reporting, providing templates for communicating findings to executives and legal teams. Finally, it aims to future-proof the reader’s knowledge by exploring strategies relevant to Windows 11 and emerging threats, including those involving AI.
Setup, Support and Ownership
Setup for this product involves the reader’s own learning environment. The book assumes access to a Windows system and likely recommends or references specific forensic tools like Volatility, FTK Imager, and PowerShell for the hands-on tutorials. There is no mention of required accessories or complex upgrade paths; ownership is about acquiring and applying the knowledge within. As an independently published book, support channels from the publisher or author are not specified in the provided data. The long-term value comes from the foundational and advanced techniques covered, which are intended to remain relevant, though the dynamic nature of cybersecurity means some tool-specific details may evolve over time. Readers must rely on the community and their own practice to supplement the core material.
What Owners Say
At the time of this analysis, there are no buyer reviews available for this title. This means there is no user-generated feedback to verify the real-world effectiveness, teaching clarity, or practical value of the content as experienced by readers. The absence of reviews makes it difficult to assess the book’s reception among its target audience of IT professionals and cybersecurity analysts. Prospective buyers must base their decision solely on the described content, features, and the author’s approach as presented in the editorial summary and specifications.
Pros and Cons
Pros
- Covers a wide range of DFIR topics in one consolidated resource.
- Includes hands-on tutorials and checklists for practical skill building.
- Emphasizes critical correlation between memory, registry, and log data.
- Addresses anti-forensic tactics and rapid containment strategies.
- Provides real-world case studies for applied learning.
- Focuses on reporting skills for executive and legal communication.
Cons
- Assumes some prior technical knowledge of Windows systems.
- No user reviews available to verify real-world effectiveness or teaching quality.
- Limited exclusively to Windows platforms.
- As an independent publication, support structures are not defined.
- Some tool-specific instructions may become dated as software updates.
- The practical value depends heavily on the reader’s ability to replicate the exercises.
Who Should Buy It (and Who Should Skip It)
This book is ideally suited for IT professionals, system administrators, and cybersecurity analysts who already possess a foundational understanding of Windows operating systems and are looking to specialize or deepen their skills in digital forensics and incident response. It is a strong fit for those tasked with investigating security breaches, hunting for threats, or needing to produce forensic evidence on Windows platforms. Individuals seeking a structured guide with practical exercises in memory analysis, registry digging, and log correlation will find its focused approach valuable. For more learning resources in the security domain, explore our guide on the best cybersecurity books for beginners.
Who should skip it? Complete beginners to both Windows internals and cybersecurity concepts may find the material challenging due to its assumed base knowledge. Those seeking information on DFIR for macOS, Linux, or other operating systems should look elsewhere, as the book’s scope is strictly Windows. Readers who prefer learning from resources with established community feedback and numerous reviews might want to wait for this title to garner user impressions. Additionally, if you are looking for reviews on different types of tech gear, our tech gear section covers a broader range of products.
Final Verdict
The Bragley Johnvigs Advanced Windows DFIR Techniques book presents itself as a comprehensive and practical manual for a very specific audience. Its strength lies in its ambitious scope, aiming to take a reader from key concepts through advanced analysis and automation, all while stressing the integrated nature of forensic artifacts. The inclusion of checklists, case studies, and reporting templates adds to its potential utility as a desk reference for active practitioners. The focus on current and future Windows environments, including Windows 11 and AI-related threats, shows an intention to remain relevant.
However, the complete lack of user reviews creates a significant unknown regarding its execution, clarity, and practical effectiveness. The assumption of prior knowledge also narrows its ideal audience. For the right person—a Windows-focused security professional ready to invest time in hands-on practice—this book could serve as a valuable upskilling resource. For others, it may be too specialized or require supplementary foundational learning first. As with any technical guide, its long-term value will be determined by the reader’s commitment to applying its lessons. For further insights into expert-selected products, you can browse our main reviews hub or the cybersecurity category.
FAQs
What prior knowledge do I need for this book?
The book assumes some prior technical knowledge of Windows operating systems. Readers should be comfortable with general Windows administration concepts, navigating the file system, and have a basic understanding of cybersecurity principles. It is not designed for absolute beginners to computing or security.
Does this book cover tools I need to download?
Yes, the content references and provides tutorials for using specific DFIR tools. These include memory acquisition tools like FTK Imager and DumpIt, analysis frameworks like Volatility for memory forensics, and built-in Windows tools like PowerShell for automation and scripting. Readers will need to set up these tools in their own practice environment.
Is the content applicable to Windows 11?
The book explicitly mentions including strategies for Windows 11 and emerging threats. This suggests that the core forensic principles are taught with consideration for the latest Windows platform, though the fundamental techniques of memory, registry, and log analysis remain consistent across recent Windows versions.
How does this book handle incident response?
A significant portion of the book is dedicated to rapid threat containment and response. It covers strategies for isolating compromised systems, remediating malware, verifying eradication, and preventing re-infection. This is integrated with the forensic analysis, teaching how to use investigative findings to inform and guide the response actions effectively.
About the author

Elvis Dicki writes reviews and buying guides for CyberSecLabs.